

THE BRIND PLATFORM
Your cybersecurity compliance workspace.
From requirements and evidence to assessments, gaps, actions and audits, Brind gives your team one structured environment to manage cybersecurity compliance across entities, frameworks and countries.

Multiple frameworks
Multiple entities
One connected workflow
BUILT FROM EXPERIENCE

2.0
Brind 2.0. Rethought around how compliance job actually works.
Brind 2.0 is more than a redesign. We rebuilt the platform around what we learned from organizations, consultants and auditors using compliance processes in practice.
User interviews, real workflows and continuous testing helped us rethink what matters: creating a more flexible platform for managing multiple entities, frameworks and country-specific requirements as regulations continue to evolve.
Built on real workflows

Designed with experts

Made to adapt
1. THE COMPLIANCE WORKSPACE
Your compliance work. One connected environment.
Brind brings requirements, assessments, evidence, gaps and improvement actions into one connected workspace. Instead of managing separate files and disconnected processes, your team works with structured compliance information that stays linked throughout the compliance lifecycle.
The workspace is designed around the way compliance professionals actually work: familiar enough to navigate like a spreadsheet, but structured enough to manage complex compliance processes across teams, entities and frameworks.

2. BUILT TO SCALE
Scale your compliance, not the complexity.
Manage multiple legal entities, frameworks and country-specific requirements within the same environment. Brind gives you a consolidated view across your organization while keeping individual entities, scopes and responsibilities clearly structured.
Whether you operate in one country or across Europe, your compliance environment can adapt as your organization and regulatory landscape evolve — without rebuilding your processes from scratch.
Entities
Manage multiple legal entities while maintaining a consolidated group-level view.
Frameworks
Work with different cybersecurity frameworks within the same compliance environment.
Countries
Manage country-specific cybersecurity requirements across different regulatory environments.
IT & OT
Manage IT and OT compliance scopes separately within the same organizational environment.
Teams
Bring different teams and organizational areas into the same compliance environment.
Central evidence management
Manage uploaded and externally stored evidence from one structured compliance environment.
Evidence-to-requirement connection
Link evidence directly to the requirements and assessments it supports.
Version & history
Keep evidence and its changes traceable as your compliance work evolves.
Evidence reuse
Use existing evidence wherever it supports multiple relevant requirements.

3. EVIDENCE MANAGEMENT
Collect once.
Use where it matters.
Manage your compliance evidence in one structured environment and connect it directly to the requirements it supports, whether files are uploaded to Brind or kept in your existing document repositories.
Documents, policies, reports and other evidence remain connected to your compliance work, making them easier to find, maintain and reuse. Instead of repeatedly collecting the same information, your team can build on existing evidence wherever it supports relevant requirements.

4. BRIND AI
Let AI do the evidence-heavy work.
Reviewing large volumes of cybersecurity evidence and mapping relevant information to individual requirements is one of the most time-consuming parts of compliance. Brind AI is designed specifically to accelerate this work.
It analyzes uploaded evidence, identifies relevant information, maps it to cybersecurity requirements and prepares preliminary assessments for expert validation. Your team stays in control of what becomes part of your compliance record.
5. FRAMEWORK MAPPING
Don't start from scratch with every framework.
Cybersecurity frameworks and national regulations often address overlapping security objectives, but organizations still manage them as separate compliance exercises. The result is duplicated assessments, repeated evidence collection and unnecessary manual work.
Brind connects related requirements across frameworks and country-specific regulations. Once your evidence, responses and assessments have been validated, they can be mapped and reused to support related requirements. This allows your team to build on existing compliance work instead of repeating it.

6. FROM GAPS TO IMPROVEMENT
Turn compliance gaps into progress.
Identifying a compliance gap is only the beginning. Brind gives your team a clear view of where requirements are not yet fully met, making it easier to identify what needs attention and turn those findings into improvement actions.
Identify gaps
See where requirements are not yet fully met and need further attention.
Take action
Turn identified compliance gaps into clear improvement actions.
Improve
Address gaps while keeping the underlying compliance context visible.
Reassess
Review your compliance position again as controls and supporting evidence evolve.


7. AUDIT READY
Don't rebuild everything when a new audit starts.
Your compliance work shouldn't stop where the audit begins. Brind keeps your compliance data structured, evidence-linked and up-to-date so you can demonstrate control and respond to auditor requests.
When it's time for an independent audit, you can collaborate with your auditor in a controlled environment and provide access to the relevant compliance information without rebuilding your audit documentation from scratch.
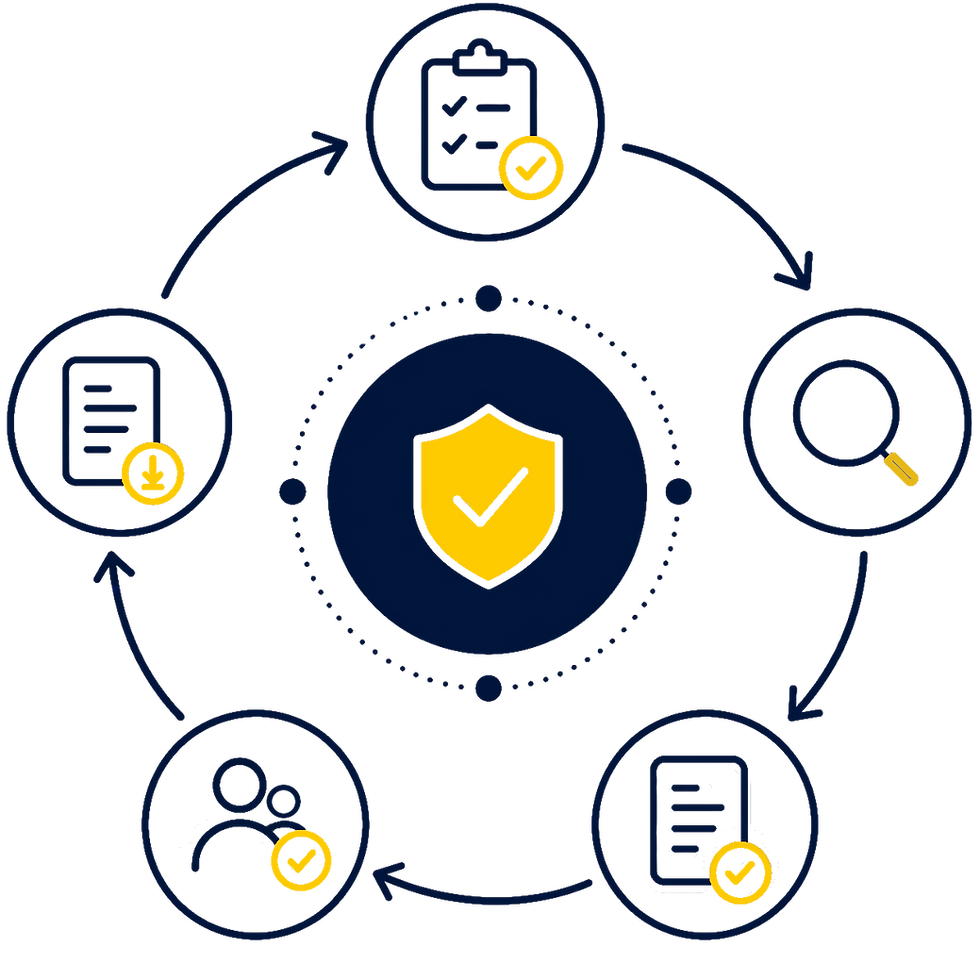
1. Centralize
All audit-related compliance data in one structured workspace.
3. Verify
Link responses to supporting evidence for easier verification.
5. Export
Keep auditor-prepared reports in Brind and export them whenever needed.
2. Track
Every change, comment and update is logged and traceable.
4. Collaborate
Give auditors access to what they need and keep everyone aligned.
BE ALWAYS AUDIT READY
8. SECURITY & CONTROL
Your compliance data. Your control.
Cybersecurity compliance involves sensitive information about your organization, systems and controls. Brind is designed to keep that information protected and separated while giving you control over who can access it and where your compliance data is stored.
Isolated environments
Customer environments and data are separated to prevent access across organizations.

Compliance
Designed to meet strict regulatory requirements, such as the GDPR, NIS2, the CRA, and the AI Act.

Security by design
Brind is built with enterprise-grade security at its core to protect your data and keep you in control.

Private AI
Brind AI keeps your data private and isolated throughout AI processing.

Your data. Your choice.

SaaS
Full functionality in Brind’s EU cloud. Platform, evidence and AI together.

Hybrid
Keep evidence in your existing repositories. Connect without sharing sensitive files.

On-prem
Run Brind entirely in your infrastructure. Maximum control over your environment.
See how Brind fits your needs.
Tell us about your organization, frameworks and compliance setup. We’ll show you how Brind can support your work.